AI Governance & Security
AI Governance in Digital Agencies: Policies, AI Literacy and Controls under the EU AI Act
Artificial intelligence is now part of everyday workflows in marketing, software development, data analysis and content production. For companies choosing a digital partner, however, the question should no longer be simply “Does our agency use AI?”, but rather “How does it use AI, what happens to our data and what controls are in place?”
In brief
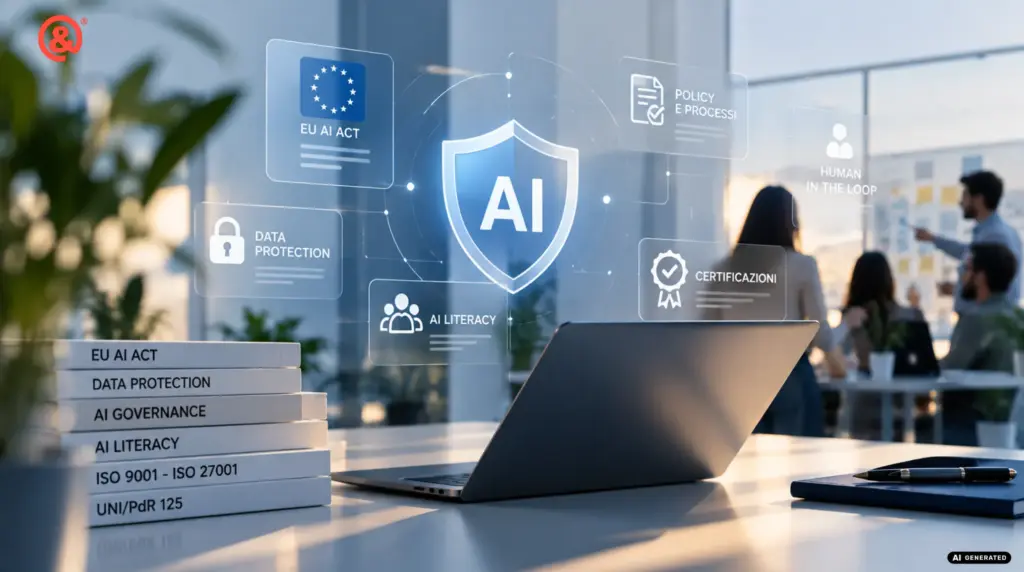
- Under Article 4 of the EU AI Act, providers and deployers of AI systems must take measures to support the development of AI literacy among staff and other people operating AI systems on their behalf.
- The 2026 Digital Omnibus on AI confirmed this obligation while clarifying that organisations are not required to guarantee a specific level of AI literacy for every individual.
- AI Governance turns legal, security and organisational requirements into practical rules: approved tools, permitted data, role-based training, human oversight and incident management.
- One of the most common organisational risks is Shadow AI: employees using unauthorised AI tools or approved tools in ways that expose confidential or client information.
- For companies selecting a digital partner, AI governance is becoming an additional indicator of organisational maturity, alongside cybersecurity, quality management and data protection.
Do you know what happens to your data when your agency uses AI?
ChatGPT, Claude, Gemini, Copilot and other AI-based systems have rapidly become part of professional workflows.
In 2026, it would probably be more unusual to find a digital agency that does not use artificial intelligence than one that uses it every day.
The real issue is therefore no longer whether an agency uses AI.
Companies should ask a different set of questions before entrusting a partner with their data, platforms, campaigns, source code or business information.
What information is entered into AI systems, which tools are approved, who checks the outputs and who remains accountable for the final work?
Uncontrolled use of AI can introduce risks involving data protection, confidential information, intellectual property, inaccurate outputs, model hallucinations, cybersecurity and regulatory compliance.
At HT&T Consulting, we therefore chose to treat artificial intelligence not simply as another productivity tool, but as a governance issue.
We have implemented an internal AI Management System and AI Governance framework covering policies, responsibilities, risk assessment, authorised tools, human oversight and a formal AI literacy programme.
What is AI Governance?
AI Governance is the set of policies, responsibilities, processes and controls an organisation uses to manage the use of artificial intelligence.
For a digital agency, this includes deciding which AI tools may be used, what information may be processed, how new systems and vendors are assessed, how employees are trained, which outputs require human review and how incidents or inappropriate uses are handled.
This approach is consistent with the broader concept of an Artificial Intelligence Management System.
The international standard ISO/IEC 42001, for example, specifies requirements for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System within an organisation.
Implementing an internal AI Management System does not automatically mean being ISO/IEC 42001 certified.
Certification is a separate assessment and certification process. The underlying management principle, however, is relevant to any organisation: AI should be governed as a business process rather than treated as an uncontrolled collection of tools.
Shadow AI: one of the hidden risks inside organisations
One of the most underestimated risks for companies is Shadow AI: the use of AI services outside approved corporate policies, processes or technology environments.
For example, an employee might upload a client document to a free AI service, paste proprietary source code into a chatbot, analyse CRM data using an unapproved platform or share information covered by a confidentiality agreement.
The problem is not necessarily the technology itself.
The problem is using technology without clear rules defining what may be done with it and which information may be processed.
AI Governance should therefore begin with a clear classification of tools, environments, use cases and information.
A practical AI tool classification model
HT&T’s internal policy classifies AI environments according to the level of organisational control, the characteristics of the service and the type of data that may be processed.
Class A: Managed business environments
Tools and business licences selected for professional use and configured according to corporate policies.
These environments are preferred for operational activities requiring higher levels of control, subject to the specific terms of the service and internal information-handling rules.
Class B: Approved public tools
These tools may only be used for activities compatible with their risk classification.
Personal data, credentials, proprietary code, confidential client information or documents covered by NDAs must not be entered where the relevant service conditions or internal policies do not allow it.
Class C: Unapproved tools
These tools cannot be used for business operations until the appropriate assessment has been completed.
Introducing a new AI service is therefore not simply a matter of individual preference: it requires an organisational evaluation.
The goal is not to prevent employees from using artificial intelligence.
AI Governance creates the conditions that allow organisations to use AI more confidently and consistently.
AI Literacy: knowing how to use ChatGPT is not enough
Article 4 of the EU AI Act introduces an important requirement for organisations that provide or deploy AI systems.
Providers and deployers must take measures to support the development of AI literacy among their staff and other people dealing with the operation and use of AI systems on their behalf.
Those measures should take into account factors such as technical knowledge, experience, education, training and the context in which AI systems are used.
Article 4 has applied since 2 February 2025, while national market surveillance authorities are responsible for supervision and enforcement under the applicable enforcement framework.
What changed with the 2026 Digital Omnibus on AI?
Regulation (EU) 2026/1744 amended Article 4 while preserving AI literacy as an obligation for providers and deployers.
The revised wording clarifies an important point: organisations must take measures to support AI literacy, but they are not required to guarantee a specific level of AI literacy for each individual employee.
In practical terms, organisations need an approach appropriate to their people, AI systems, activities and risks.
A marketer, project manager, software developer and governance officer do not need the same AI training.
For this reason, HT&T has implemented a role-based AI literacy programme covering different levels of knowledge and operational responsibility.
AI-1 — Foundation
Core AI principles, privacy, security, compliance, responsible use, key risks and internal company rules.
AI-2 — Operational
Professional use of generative AI, prompting techniques, output validation, hallucination management, fact-checking and applications in marketing, communication and project management.
AI-3 — Advanced
API integrations, automation, Retrieval-Augmented Generation, AI agents, interoperability protocols, software development and security considerations related to AI systems.
AI-4 — Governance
Risk assessment, vendor assessment, internal audits, oversight, incident management, policy updates and continuous monitoring of the AI governance framework.
For a broader overview of the regulatory framework, transparency requirements and implementation deadlines, read our guide to the EU AI Act for businesses, chatbots and AI-generated content.
A note on the Italian regulatory context
HT&T is an Italian company operating within both the European and Italian regulatory frameworks.
Italy’s Law No. 132 of 23 September 2025 introduced national provisions concerning artificial intelligence.
Among other measures, Article 13 addresses the use of AI in intellectual professions and requires professionals to provide clients with clear, simple and comprehensive information concerning the AI systems used in the professional activity.
For international clients, the broader lesson is relevant beyond Italy: transparency about how AI is used is increasingly becoming part of the trust relationship between companies and their professional partners.
Human Oversight: AI can assist, but accountability remains human
One of the principles of our AI Governance framework is that artificial intelligence does not automatically replace professional responsibility.
A generative model can accelerate research, suggest copy, support software development, identify patterns or process large volumes of information.
That does not mean its output should automatically be treated as correct.
An AI output is an input for a professional. It is not a transfer of accountability.
Depending on the activity, HT&T therefore applies human review processes such as editorial review, fact-checking, code review, data validation or approval by the person responsible for the project.
This becomes particularly important when AI-assisted outputs are delivered to clients or published externally.
Transparency, AI-generated content and Article 50
Article 50 of the EU AI Act establishes transparency requirements for specific AI systems and use cases.
These include requirements concerning certain AI-generated or manipulated outputs, interactions with AI systems, deepfakes and specific content intended to inform the public.
This does not mean that every piece of content created with AI assistance must carry the same label in every situation.
Requirements depend on the role of the organisation, the type of AI system, the type of content and how it is used.
For some text published to inform the public, the regulatory framework also considers situations in which content undergoes human review or editorial control and a natural or legal person retains editorial responsibility.
At the same time, technologies such as C2PA and Content Credentials are helping create a technical infrastructure through which the origin and modification history of digital content can be made verifiable.
We explored this topic in greater detail in our guide to C2PA and Content Credentials
, including how provenance metadata, digital signatures and emerging durable credentials can help make the origin of digital content more verifiable.
AI Governance should not operate separately from information security
An AI Management System is useful only if it is connected to the rest of the organisation.
AI Governance should interact with existing processes for information security, access control, vendor management, employee training, incident management, business continuity, quality management and data protection.
At HT&T, the AI Governance framework builds on an established certified management environment that includes ISO 9001 for quality management, ISO/IEC 27001 for information security, ISO/IEC 27017 and ISO/IEC 27018 for cloud security and protection of personal information in cloud environments, together with other organisational governance standards.
We explain this organisational model in more detail in our overview of HT&T as an ISO-certified digital agency
, where we describe how quality management, information security and organisational governance work together.
The principle is straightforward: AI governance should become part of the organisation’s existing system of controls rather than another isolated policy document.
How can you tell whether a digital agency uses AI safely?
When selecting a digital agency or technology partner, companies increasingly need to assess how that supplier uses artificial intelligence.
Asking “Do you use AI?” tells you very little.
More useful questions include:
AI Governance checklist for evaluating a digital partner
- Does the agency have a formal AI policy?
- Are AI tools assessed and approved before employees use them?
- Are there clear rules defining which categories of data may or may not be processed by AI systems?
- Is there a process for evaluating new AI vendors and services?
- Does the agency provide formal AI literacy training?
- Is training adapted to different roles and risk levels?
- Are AI-generated outputs reviewed by people where appropriate?
- Are there procedures for reporting and managing AI-related incidents or inappropriate use?
- Are responsibilities for AI use clearly assigned?
- Are AI governance, privacy, cybersecurity and information security managed together?
A mature digital supplier should be able to answer these questions clearly rather than simply stating that it uses “enterprise AI” or “secure AI tools”.
What does AI Governance actually change for the client?
An AI Management System should not exist merely to create policies and documentation.
It should change the way work is carried out.
Controlled Data → Controlled Tools → Verified Outputs → Human Accountability
Greater control over client information
Employees know which information may be used in different AI environments and which data requires additional protection or must not be transferred to external services.
Lower Shadow AI risk
The adoption of new AI tools is governed by the organisation rather than left entirely to individual decisions.
More reliable outputs
Validation, fact-checking and human oversight reduce the risk of incorrect generative outputs reaching clients or being published.
Clear accountability
AI supports professional work without removing responsibility from the people and organisations delivering the service.
Better traceability
Policies, assessments, training records and operating procedures make it easier to understand how AI is being used across the organisation.
Good AI Governance makes it easier to use AI well
Policies, approvals and controls may appear to make artificial intelligence harder to use.
In practice, the opposite can happen.
Without rules, organisations often move between two extremes: allowing employees to use almost any AI service without oversight or blocking AI because the risks appear too difficult to manage.
A structured governance framework creates an environment in which experimentation and innovation can take place with clearer boundaries.
Governing AI does not necessarily mean using it less. It means being able to use it more deliberately because the organisation understands the boundaries.
When choosing a digital partner, ask how they govern AI
Artificial intelligence can improve productivity, accelerate analysis and support innovation.
Technology alone, however, tells you very little about the quality of the process behind its use.
A company entrusting a partner with data, digital platforms, source code, advertising campaigns, analytics, content and strategy should therefore also consider that partner’s maturity in the use of artificial intelligence.
It is not enough to know which AI tools the agency uses.
Companies should understand what information can be processed, which controls are applied, how employees are trained, how new systems are assessed and who remains accountable for the outputs.
That is the principle we have applied at HT&T Consulting: using artificial intelligence as an amplifier of professional expertise while maintaining governance, security and human oversight.
You can also learn more about HT&T Consulting’s approach to digital strategy, data, performance and certified project governance.
Looking for a digital agency with structured processes and strong data protection practices?
HT&T supports companies across digital development, ecommerce, performance marketing, data, automation and artificial intelligence.
Our approach combines innovation with information security, governance and human accountability, helping organisations build digital projects that are consistent with their goals, data and risk profile.
Frequently asked questions about AI Governance
What is an AI Management System?
An AI Management System is a structured set of policies, responsibilities, processes and controls used by an organisation to govern the introduction and use of artificial intelligence. It can cover AI inventories, risk assessment, staff training, human oversight, vendor management and incident procedures.
Does the EU AI Act require companies to provide AI training?
Article 4 of the EU AI Act requires providers and deployers of AI systems to take measures to support the development of AI literacy among staff and other people operating or using AI systems on their behalf. Measures should take account of technical knowledge, experience, education, training and the context in which the systems are used.
Does every company need an AI policy?
The EU AI Act does not simply state that every company must create a document called an “AI Policy”. However, organisations using AI need practical measures to manage obligations, risks, responsibilities and AI literacy. A formal AI policy can be an effective way to define approved tools, permitted data, responsibilities, training requirements, human review and incident procedures.
What changed with the 2026 Digital Omnibus on AI?
Regulation (EU) 2026/1744 amended several parts of the AI Act. Regarding AI literacy, it maintained the obligation for providers and deployers to take measures supporting AI literacy while clarifying that they are not required to guarantee a specific level of AI literacy for each individual.
Are an internal AI Management System and ISO/IEC 42001 certification the same thing?
No. An organisation may establish its own AI Management System or governance framework. ISO/IEC 42001 is an international standard specifying requirements for an Artificial Intelligence Management System. Certification against ISO/IEC 42001 is a separate formal assessment and certification process.
Can a digital agency enter client data into ChatGPT or other AI tools?
There is no single answer that applies to every tool, account configuration or category of data. Organisations must consider the information involved, service terms, account settings, contractual obligations, data protection requirements and internal policies. This is why a mature AI governance framework defines which environments may be used and which categories of information are permitted.
What is Shadow AI?
Shadow AI is the use of artificial intelligence tools or services outside an organisation’s approved processes, systems or policies. It can increase the risk of confidential information, personal data, intellectual property or proprietary code being handled inappropriately.
How should a company evaluate a digital agency’s use of AI?
Useful indicators include formal AI policies, approved-tool processes, data-handling rules, vendor assessment, role-based AI literacy programmes, human oversight, incident management and integration between AI governance, privacy and information security. Relevant information-security certifications can provide additional evidence of organisational maturity.
Official sources and further reading
European Artificial Intelligence Act
Official text of Regulation (EU) 2024/1689 laying down harmonised rules on artificial intelligence.
European Commission — AI Literacy
European Commission guidance and information on AI literacy requirements under Article 4 of the AI Act.
Digital Omnibus on AI
Regulation (EU) 2026/1744 amending parts of the EU AI Act, including Article 4 on AI literacy.
ISO/IEC 42001
International standard specifying requirements for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System.
Italian Law No. 132/2025
Italian national provisions concerning artificial intelligence, relevant to HT&T’s domestic regulatory environment.
Continua a leggere
17 minutes of reading
11 minutes of reading
And it consumes less energy.
To return to the page you were visiting, simply click or scroll.